Binance Reveals How a Rp100 Trillion Hack Happened: Fake Job Interviews and AI
Baca dalam 60 detik
- Peretas mengeksploitasi proses rekrutmen dan perangkat lunak pengembang untuk menembus infrastruktur dompet Binance.
- Kerugian awal US$6,34 miliar, namun Binance mengklaim telah memulihkan 98% aset terdampak.
- Insiden ini memicu pertanyaan tentang ketahanan keamanan bursa terpusat dan pengawasan regulator di Indonesia.
Binance revealed that the cyberattack that drained more than US$6 billion from its wallet systems on October 29 was not a single breach but a long operation exploiting gaps in both people and technology. Binance Co-CEO Richard Teng said the hackers spent months building an entry path through fake job interviews and modified developer software.
In an interview with CNBC, Teng dismissed the notion that the incident was caused by one employee's negligence. He laid out the chronology: in June, the attackers prepared a fake version of a developer tool and persuaded an engineer to install it. Two months later, they posed as recruiters and held a series of job interviews with another engineer, culminating in a coding test containing hidden malware. From that point, according to Teng, the hackers moved aggressively through internal AI tools and gained access to the wallet's transaction authorization system.
Binance's security report said the incident began when a DevOps engineer downloaded a modified Homebrew installation to install a popular AI coding tool. The company detected suspicious activity, replaced devices, and rotated credentials, but the role of that engineer and their colleagues on the wallet infrastructure team had already been exposed. The attack is one of the largest cryptocurrency asset breaches in history, surpassing similar cases at other exchanges.
"We also engaged independent experts to review all the steps we have taken, and we will continue to strengthen our defenses as the investigation proceeds," Teng said, adding that Binance is working with law enforcement and industry partners to trace and freeze the stolen funds.
Despite the massive scale of the losses, Binance insists its financial condition remains solid. The company has rebuilt the affected wallet systems and internal AI tools, replaced compromised devices, disabled related credentials and tokens, and expanded security scanning on employee devices. Some withdrawals remain temporarily restricted, and Binance has promised to cover all customer losses using internal reserves.
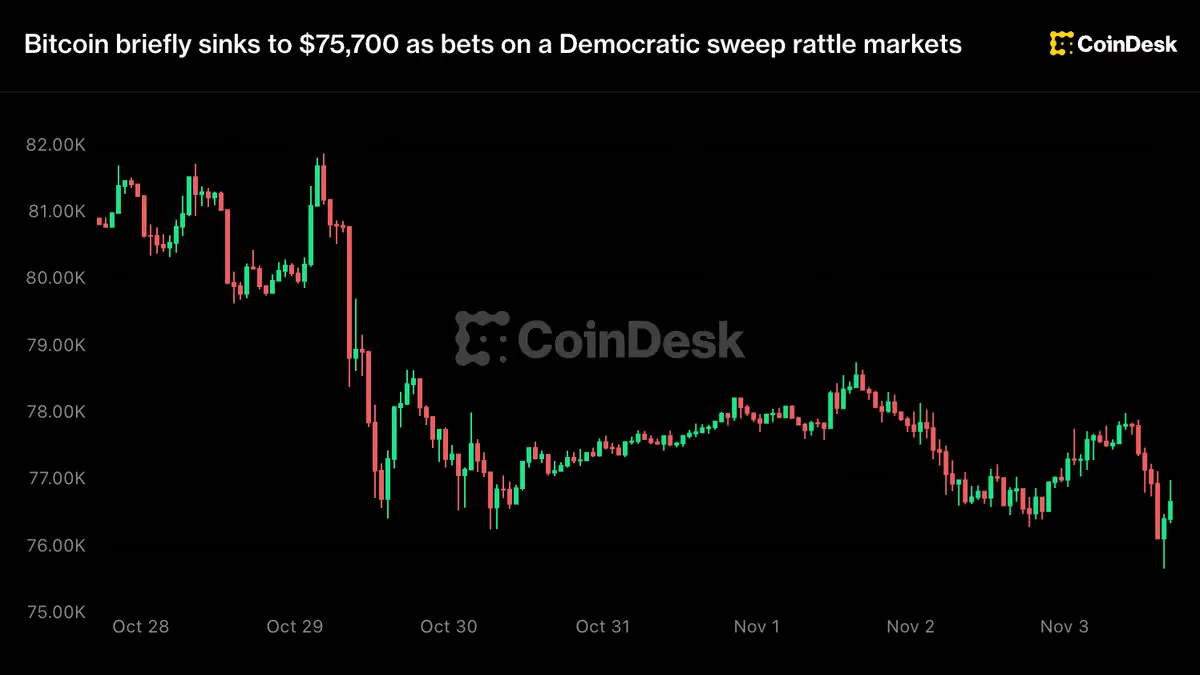
The impact on the global cryptocurrency market was brief. Unlike previous collapses of major exchanges that triggered prolonged panic, this shock subsided relatively quickly. However, market participants are now watching whether Binance can fully restore trust in centralized exchanges, especially amid rising cyberattacks targeting digital asset custody infrastructure.
For Indonesia, this case is a stark warning. The Financial Services Authority (OJK), which has supervised crypto assets since early 2025, needs to scrutinize the security models of local exchanges, including recruitment practices and employee access management. Crypto traders in the country, whose numbers keep growing, deserve assurance that their funds are not easy targets for international syndicates. Regulators are also urged to speed up the drafting of cybersecurity audit standards for crypto asset trading operators.
Looking ahead, the big question is not merely whether Binance can close the existing gaps, but how far the global crypto exchange industry is prepared to face increasingly sophisticated and multidimensional hacking tactics. Without strict oversight and sustained transparency, public trust in the digital financial ecosystem will continue to be tested.