Bitget Suspected of Being Breached by North Korean Hackers, Losses Reach Rp5.6 Trillion
Baca dalam 60 detik
- Bitget kehilangan aset digital senilai sekitar 351,6 juta dolar AS akibat akses tidak sah ke sistem backend dompet panas dan hangat.
- Indikasi awal mengarah ke kelompok peretas Korea Utara karena jejak alamat IP yang terhubung ke layanan VPN pernah dipakai aktor tersebut.
- Dana nasabah dijamin aman melalui User Protection Fund senilai lebih dari 464 juta dolar AS, tetapi penarikan masih dibekukan sementara.
Global crypto exchange Bitget announced the suspected involvement of hackers affiliated with North Korea in a breach that drained about 351.6 million US dollars, or the equivalent of Rp5.6 trillion (at an assumed exchange rate of Rp16,000), from a number of company wallets. Preliminary findings from an internal investigation pointed to an attack pattern similar to previous operations attributed to Pyongyang.
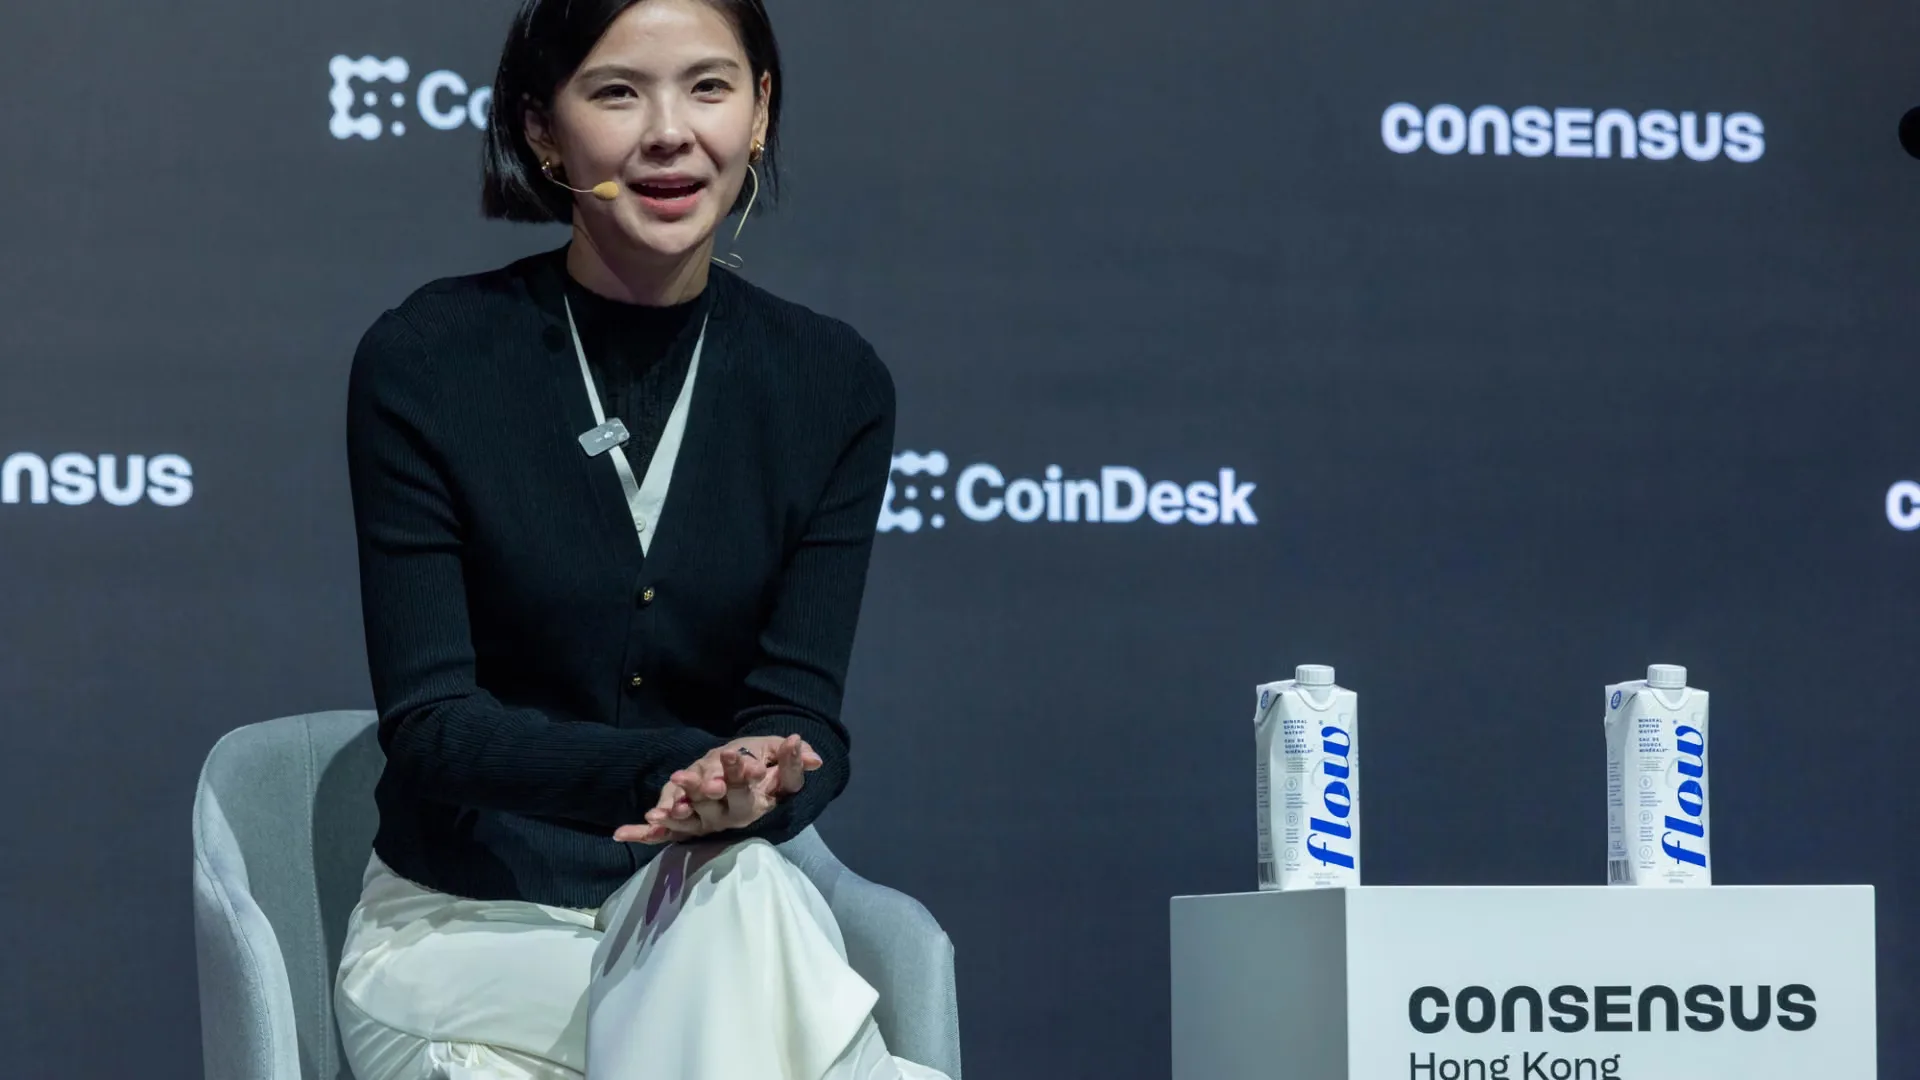
Bitget CEO Gracy Chen, in a livestream on platform X, revealed that the forensic team found an internet protocol address linked to a VPN service previously used by the North Korean hacker group. Nevertheless, the specific intrusion method that penetrated Bitget's systems is still under technical investigation. The incident was detected on Thursday afternoon US time, when 19 unauthorized transfers occurred from part of the hot wallet and warm wallet infrastructure, while the cold wallet was confirmed to remain safe.
The affected assets include ether, XRP, USDT, USDC, Avalanche, and BNB spread across the Ethereum, XRP Ledger, Avalanche, BNB Smart Chain, and Arbitrum networks. Initial on-chain estimates had cited a figure of 183 million US dollars, but Bitget considers that analysis to have not captured all cross-blockchain activity. The exchange's security team found that the attackers managed to penetrate the critical wallet backend system, falsify transfer information, and trigger Bitget's signing authorization process. Chen stressed that access had been shut down to prevent further fund flows. "Private key compromise has been ruled out," she said.
Withdrawals were temporarily halted while the technical team repairs and strengthens the affected systems. However, deposit and trading services continue to operate normally. Chen declined to give a definite timeline, but said withdrawals could resume within hours or days, and "will not take weeks". The company assured that customer balances are accurate and that the loss is fully covered by the User Protection Fund, which is worth more than 464 million US dollars.
"We identified an IP address linked to a VPN service previously used by the North Korean hacker group. This attack pattern resembles operations we have seen before," said Gracy Chen, CEO of Bitget.
Bybit CEO Ben Zhou said his team is ready to assist Bitget, just as Bitget had supported Bybit after the 1.5 billion US dollar hack in February 2025. Bybit is also updating the LazarusBounty platform to help track stolen funds. This incident extends the list of major cyberattacks on crypto exchanges in recent years, which are often linked to state-backed hacker groups.
For Indonesia, this event is an alarm for players in the domestic crypto asset industry. the Financial Services Authority (OJK) and Bappebti need to strengthen oversight of exchange cybersecurity standards, especially regarding private key management and transaction authorization procedures. Retail investors in the country who are increasingly active in trading crypto are also required to be more selective in choosing platforms that have protection funds and governance transparency. This incident underscores that cyber risk is not only a matter of technology, but also the stability of the national digital financial ecosystem.
Going forward, the big question is how far global crypto exchanges can close security gaps in the rarely exposed backend layer. If such attacks continue to recur, investor trust in the promise of "safe funds" could erode, and regulators in various jurisdictions, including Indonesia, may be pushed to impose stricter mandatory security standards.